AI-powered phishing and scam email warning for a Houston business cybersecurity article

How Houston Businesses Can Spot AI-Powered Scam Emails

AI changed the look of phishing emails

For years, employees were told to look for spelling mistakes in scam emails. That advice is no longer enough.

AI tools can produce clear and professional messages in seconds. As a result, attackers can create emails that sound more like normal business communication.

Therefore, employees must focus less on grammar. Instead, they should focus on what the message asks them to do.

Watch the request, not just the writing

A polished email can still be dangerous. For example, a message may ask an employee to change banking information. Another may request a password reset or verification code.

Urgency is another warning sign. Attackers often want the employee to act before checking the request.

Therefore, slow down when money, credentials, or sensitive data are involved. A short verification step can stop a costly mistake.

Verify payment and banking changes another way

Business email compromise often targets accounting teams. An attacker may imitate a vendor or compromise a real mailbox.

The email may look completely normal. However, it may contain new payment instructions controlled by the attacker.

Always verify banking changes through a second channel. For example, call a known phone number already on file. Do not use the phone number included in the suspicious message.

Protect accounts with MFA

Multi-factor authentication adds another barrier after a password. Therefore, it can reduce the damage from stolen credentials.

However, MFA is not perfect. Attackers may still try to trick users into approving a login.

For that reason, employees should never approve an unexpected authentication request. In addition, businesses should use stronger authentication methods where practical.

Use email security and employee training together

Technology can block many malicious messages. However, no filter catches every scam.

Employees provide another layer of defense. Therefore, training should use realistic examples and simple verification rules.

Also, make reporting easy. Employees should know exactly where to send a suspicious message. A fast report can help IT protect other users before they click.

Build a simple verification culture

The best process does not depend on employees becoming security experts. Instead, give them clear rules.

For example, verify changes to payment information. Confirm unusual requests from executives. Never share a verification code by email or phone.

Graphene Technologies provides cybersecurity services for Houston businesses. We can help with email security, MFA, endpoint protection, monitoring, and user awareness. Schedule a free 30-minute IT assessment to identify your biggest security gaps.

Call to Action

Need a clearer picture of your IT risks and priorities? Schedule a Free 30-Minute IT Assessment with Graphene Technologies. We will review your current environment and identify practical next steps.

OneDrive versus SharePoint file storage comparison for Houston businesses using Microsoft 365

OneDrive vs. SharePoint: Where Houston Businesses Should Store Files

OneDrive and SharePoint solve different problems

OneDrive and SharePoint both store files in Microsoft 365. However, they are designed for different types of work.

OneDrive is primarily an individual’s workspace. SharePoint is designed for team and company information.

That difference matters because file ownership affects access and continuity. Therefore, choosing the right location can prevent problems when employees change roles or leave.

Use OneDrive for individual working files

OneDrive works well for documents that one employee owns while creating or editing them. For example, drafts and personal working notes often belong there.

In addition, OneDrive makes those files available across approved devices. Employees can also share a file when collaboration is temporary.

However, OneDrive should not become the permanent home for important department records. If the business depends on a file, move it to a team-owned location.

Use SharePoint for team and company information

SharePoint works better for files that belong to a department, project, or the company. Examples include procedures, templates, marketing assets, and shared operational documents.

Because SharePoint belongs to the organization, access does not depend on one employee’s account. As a result, the business keeps control when staffing changes.

SharePoint also supports structured permissions. Therefore, teams can provide access based on roles instead of sharing files one person at a time.

Avoid the most common storage mistake

A common mistake is storing critical company files inside one employee’s OneDrive. At first, the setup seems convenient. However, problems appear when that employee leaves.

The business may then need to recover ownership, repair links, and rebuild access. In addition, coworkers may not know which files are current.

Instead, move shared business information to SharePoint. Then, use OneDrive for personal work in progress.

Keep permissions simple

Permissions become difficult when businesses create too many exceptions. Therefore, use groups whenever possible.

For example, create access around departments or job roles. Then, add and remove employees from those groups as responsibilities change.

Also, review external sharing regularly. Old sharing links can remain active long after a project ends. A recurring review helps remove access that is no longer needed.

Plan the structure before moving everything

Do not move years of files into SharePoint without a plan. First, decide which information belongs to each team. Next, remove duplicates and outdated content.

Then, create a simple folder and site structure. Keep names clear because employees need to find information quickly.

Graphene Technologies provides Microsoft 365 consulting for Houston businesses. We can help with OneDrive, SharePoint, permissions, migrations, backup, and security. Schedule a free 30-minute IT assessment to review your Microsoft 365 environment.

Call to Action

Need a clearer picture of your IT risks and priorities? Schedule a Free 30-Minute IT Assessment with Graphene Technologies. We will review your current environment and identify practical next steps.

Microsoft 365 outage planning for a Houston business with a service interruption warning

Microsoft 365 Outage Plan: How Houston Businesses Can Keep Working

Microsoft 365 is reliable, but outages still happen

Microsoft 365 supports email, Teams, OneDrive, SharePoint, and many daily workflows. Therefore, even a short outage can affect a large part of the business.

The problem is simple. When Microsoft has a service issue, your team may not be able to fix it. Instead, you must wait while Microsoft restores the service.

However, waiting does not have to mean stopping. A basic continuity plan can keep employees communicating and customers informed.

Start with the services you cannot operate without

First, list the Microsoft 365 services that matter most. For many businesses, Outlook and Teams will be near the top. SharePoint and OneDrive may also be critical.

Next, identify the work that stops when each service fails. For example, an Outlook outage may interrupt customer communication. A SharePoint outage may block access to procedures or shared documents.

This exercise creates priorities. As a result, your team knows which backup process to use first.

Create a backup communication method

Next, decide how employees will communicate if Teams or Outlook is unavailable. A group text system may work for a small team. Larger businesses may need another approved communication platform.

However, do not wait until the outage to choose the tool. Employees should know the process in advance.

Also, keep key customer and vendor phone numbers somewhere accessible. That way, your team can still communicate when cloud contacts are unavailable.

Keep critical information available

Some information should remain accessible during an outage. For example, keep emergency contacts, key procedures, and critical vendor details available offline.

In addition, decide which documents need an alternate copy. Do not copy every file. Instead, focus on the information needed to operate for several hours.

A Microsoft 365 support provider in Houston can help identify those dependencies. More importantly, the provider can help keep the plan practical.

Know how to confirm an outage

When users report a problem, first determine whether the issue is local. Check internet connectivity and test another service.

Then, review Microsoft’s service-health information. Your IT provider can also confirm whether other customers see the same issue.

This matters because the response changes based on the cause. If Microsoft has an outage, your team should activate the continuity plan. If the problem is local, your IT team should troubleshoot it.

Do not confuse availability with backup

Microsoft 365 availability and Microsoft 365 backup solve different problems. An outage affects access to the service. By contrast, backup helps recover deleted or damaged data.

Therefore, businesses should plan for both. Use a continuity plan for service interruptions. In addition, maintain a recovery strategy for important Microsoft 365 data.

Graphene Technologies helps Houston businesses manage Microsoft 365, security, backup, and business continuity together. Schedule a free 30-minute IT assessment to review your current plan.

Call to Action

Need a clearer picture of your IT risks and priorities? Schedule a Free 30-Minute IT Assessment with Graphene Technologies. We will review your current environment and identify practical next steps.

Monthly IT checklist for a Houston small business covering backups, updates, security, users, and devices

The 30-Minute IT Check Every Houston Small Business Should Do Once a Month

Why a monthly IT check matters

Technology problems rarely appear without warning. However, many businesses notice the warning only after work stops. A backup may fail for weeks. An employee account may stay active after someone leaves. Likewise, a laptop may miss important security updates.

A short monthly review can catch those issues early. Therefore, the goal is not to fix every problem in 30 minutes. Instead, use the time to find problems and assign the next action.

For Houston businesses, this routine can also reduce surprise IT costs. More importantly, it gives owners a clearer view of their technology. That visibility makes planning easier.

1. Check updates and patching

First, review operating-system and application updates. Look for computers that keep asking for a restart. Also, check devices that have not reported in recently.

Updates matter because attackers often target known weaknesses. Once a vendor releases a fix, businesses should install it promptly. However, updates can fail or get delayed. A monthly check helps you spot those exceptions.

If you use managed IT services in Houston, ask your provider for a patching report. The report should show both successful updates and devices that need attention.

2. Confirm backups are actually working

Next, open your backup dashboard. Do not rely only on a green status icon. Instead, review recent jobs and look for repeated warnings.

Then, confirm that important Microsoft 365, server, and business data is protected. In addition, test a small restore from time to time. A successful backup is useful only when you can recover the data.

If a restore fails, document the issue immediately. After that, assign someone to correct it before the next monthly review.

3. Review users and access

Afterward, review user accounts in Microsoft 365 and other critical systems. Every active account should belong to someone who still needs access.

Former employees should not remain active. Likewise, employees should not have administrator rights without a business reason. Excess access increases risk because one compromised account can expose more systems.

Also, confirm that multi-factor authentication is enabled. Pay special attention to administrators, finance staff, and anyone who can change payment information.

4. Look at devices and security alerts

Next, review the devices connected to your environment. Identify laptops, phones, or other systems that you do not recognize.

At the same time, check endpoint-security alerts. One unresolved alert may be harmless. However, repeated alerts can point to a larger problem.

Finally, review your firewall, security tools, and monitoring dashboard. If nobody checks the alerts, the tools cannot protect the business effectively.

5. Review licenses and recurring IT problems

Finally, review technology subscriptions and recurring support issues. Businesses often keep paying for old licenses after employees leave. Similarly, they may pay for two tools that solve the same problem.

Then, look at recent help-desk requests. If the same problem appears every month, stop treating it as a one-time ticket. Instead, identify the root cause.

This step can lower costs. In addition, it helps your team spend less time fighting the same technology problem.

Make the 30-minute check a routine

Put the review on the calendar for the same day each month. For example, use the first Monday morning. Then, keep a short record of what you found.

Over time, patterns will become clear. As a result, you can prioritize upgrades and security improvements with better information.

Graphene Technologies helps Houston businesses manage this process through proactive IT support, cybersecurity, Microsoft 365 management, and business continuity planning. If you want a second set of eyes, schedule a free 30-minute IT assessment.

Call to Action

Need a clearer picture of your IT risks and priorities? Schedule a Free 30-Minute IT Assessment with Graphene Technologies. We will review your current environment and identify practical next steps.

Modern managed IT support illustration featuring secure business technology, cloud connectivity, network infrastructure, and cybersecurity for Houston businesses.

Why Houston Businesses Are Switching to Proactive Managed IT Support

Technology is no longer just a support function—it drives communication, operations, customer service, accounting, and revenue. As businesses grow, they often discover that calling an IT technician only after something breaks creates unnecessary downtime, unpredictable expenses, and security risks. Consequently, many organizations are replacing reactive support with proactive managed IT services. At Graphene Technologies, we help companies throughout Houston improve reliability, strengthen cybersecurity, and align technology with business goals.

Why Break-Fix IT No Longer Works

Traditional break-fix support waits for a problem before taking action. Although this approach may appear less expensive, the hidden costs quickly add up. Employees lose productivity, customers experience delays, and emergency repairs usually cost more than preventive maintenance. Therefore, businesses are looking for a smarter approach.

What Is Proactive Managed IT?

A proactive managed IT provider continuously monitors networks, servers, computers, Microsoft 365, backups, and cybersecurity tools. Instead of reacting to failures, technicians identify issues early and resolve them before they disrupt operations. Furthermore, businesses benefit from predictable monthly costs and strategic technology planning.

Benefit 1: Less Downtime

First, proactive monitoring reduces unexpected outages. Automated alerts identify hardware failures, storage issues, failed backups, and unusual activity before they become major problems. As a result, employees spend more time working and less time waiting for systems to be repaired.

Benefit 2: Stronger Cybersecurity

Cyber threats continue to evolve. Therefore, proactive IT support includes endpoint detection, email security, vulnerability management, patching, and continuous monitoring. In addition, regular security reviews help organizations reduce ransomware and phishing risks.

Benefit 3: Predictable IT Costs

Emergency repairs can quickly become expensive. By contrast, managed IT services provide predictable monthly pricing that simplifies budgeting while reducing costly surprises.

Benefit 4: Better Employee Productivity

When computers, Wi-Fi, Microsoft 365, printers, and cloud applications work consistently, employees remain productive. Likewise, a responsive help desk resolves issues quickly so teams can stay focused on serving customers.

Benefit 5: Strategic Technology Planning

Technology decisions should support long-term growth. Consequently, managed IT providers help businesses budget for upgrades, plan hardware replacements, evaluate cloud solutions, and improve business continuity.

Signs It’s Time to Switch

Consider managed IT if your employees regularly report slow computers, recurring Wi-Fi issues, aging hardware, failed backups, cybersecurity concerns, or frequent emergency support calls. Moreover, businesses preparing for compliance or growth often benefit from proactive IT management.

Choosing the Right IT Partner

Look for a provider that offers 24/7 monitoring, cybersecurity expertise, Microsoft 365 support, backup and disaster recovery, responsive help desk services, strategic consulting, and clear communication. Above all, choose a partner that understands your business objectives rather than simply fixing technical issues.

Conclusion

Overall, proactive managed IT support helps businesses reduce downtime, improve security, and plan for future growth. Instead of waiting for technology to fail, organizations can invest in prevention, monitoring, and continuous improvement. If your business is ready for dependable IT Support in Houston, Graphene Technologies can help create a technology strategy that supports your long-term success.

Frequently Asked Questions

Q: Is managed IT more expensive than break-fix?
A: Although there is a monthly investment, most businesses save money through fewer outages, lower emergency repair costs, and improved productivity.

Q: Can managed IT support Microsoft 365?
A: Yes. Services typically include user management, security, licensing, backups, and ongoing support.

Q: Do small businesses benefit from managed IT?
A: Absolutely. Small businesses often gain enterprise-level support without hiring an internal IT department.

Cybersecurity illustration featuring a security shield, cloud protection, laptop, and secure network infrastructure representing proactive cybersecurity services for businesses.

The 2026 Cybersecurity Checklist Every Houston Business Should Complete

Cyber threats continue to evolve, and businesses of every size are being targeted. Fortunately, organizations can reduce their exposure by following proven security practices. In this guide, you’ll find ten practical steps that improve security, reduce downtime, and strengthen business resilience. Moreover, each recommendation is designed for small and midsize businesses that rely on Microsoft 365 and cloud technology.

1. Enable Multi-Factor Authentication

First, require multi-factor authentication (MFA) for every employee. In addition, protect administrator accounts with stronger authentication methods. As a result, stolen passwords become much less valuable to attackers.

2. Keep Systems Updated

Next, install security updates for Windows, Microsoft 365 Apps, servers, browsers, and network equipment. Although updates can be inconvenient, they close known vulnerabilities before criminals exploit them.

3. Secure Microsoft 365

Review Conditional Access, Microsoft Defender, mailbox forwarding rules, external sharing, and legacy authentication. Furthermore, disable unused accounts and verify that privileged users follow stricter security policies.

4. Review User Permissions

Employees often change responsibilities over time. Therefore, review permissions for SharePoint, OneDrive, HR folders, finance systems, and network shares. Finally, remove unnecessary access by following the principle of least privilege.

5. Verify Your Backups

Backups are only valuable if they work. For that reason, test file restores and server recovery regularly. Likewise, maintain an immutable or offline backup copy to improve ransomware recovery.

6. Protect Every Endpoint

Deploy endpoint detection and response, encryption, and business-grade firewall protection. In addition, replace unsupported devices before they become a security risk.

7. Train Employees

Technology alone cannot stop every attack. Instead, provide ongoing security awareness training. For example, teach employees how to recognize phishing emails, fake invoices, QR-code scams, and suspicious links.

8. Strengthen Network

Secure wireless networks with strong encryption and separate guest traffic from business traffic. Meanwhile, monitor network activity to identify unusual behavior before it becomes a larger problem.

9. Monitor Continuously

Continuous monitoring improves visibility across your environment. Consequently, your IT team can detect malware, failed logins, and suspicious activity much faster.

10. Create an Incident Response Plan

Finally, document who to contact, how to isolate affected devices, how to restore backups, and how to communicate with employees and customers. Above all, practice the plan before an emergency occurs.

Cybersecurity Checklist

  • Enable MFA for all users
  • Apply software updates promptly
  • Review Microsoft 365 security settings
  • Audit user permissions
  • Test backup recovery
  • Deploy endpoint protection
  • Train employees regularly
  • Secure network infrastructure
  • Monitor systems continuously
  • Maintain an incident response plan

Conclusion

Overall, cybersecurity is an ongoing process rather than a one-time project. By completing this checklist, businesses can significantly reduce their cyber risk. Furthermore, proactive security lowers downtime, protects customer trust, and supports long-term growth. If your organization needs help implementing these recommendations, Graphene Technologies can provide managed cybersecurity, Microsoft 365 security, and proactive IT support throughout the Houston area.

Microsoft Copilot security illustration showing AI, Microsoft 365 apps, and cybersecurity protection for secure business deployment.

How to Prepare Microsoft Copilot Without Exposing Sensitive Business Data

Artificial intelligence is changing how businesses work. Microsoft Copilot can draft emails, summarize meetings, analyze spreadsheets, create presentations, and answer questions using your organization’s Microsoft 365 data. For many businesses, it has the potential to save hours every week and improve employee productivity.

However, one question we hear from business owners throughout Houston is:

“How do we use Microsoft Copilot without exposing confidential company information?”

It’s a valid concern.

Microsoft Copilot is incredibly powerful because it can access information stored in Outlook, Teams, SharePoint, OneDrive, Word, Excel, and other Microsoft 365 applications. If your Microsoft 365 environment has poor permissions, outdated security settings, or excessive data sharing, Copilot may surface information users shouldn’t see.

The good news is that Microsoft Copilot was designed with enterprise-grade security in mind. It respects your existing Microsoft 365 permissions. If your environment is configured correctly, Copilot becomes an incredibly valuable productivity tool without increasing unnecessary risk.

At Graphene Technologies, we help organizations implement secure AI solutions through Microsoft 365 Support Houston businesses can trust. Before enabling Copilot, we recommend following the framework below.

Why Security Comes Before AI

Many organizations rush to enable AI because they want immediate productivity gains.

The reality is that AI magnifies both strengths and weaknesses.

If your Microsoft 365 environment is well organized, secure, and governed, Copilot becomes an exceptional assistant.

If your environment has years of permission issues, shared folders open to everyone, inactive accounts, and sensitive documents available to broad groups, AI can expose those weaknesses much faster.

That doesn’t mean Copilot is unsafe.

It means your Microsoft 365 environment should be prepared before deployment.

Think of Copilot as a highly efficient employee. It only works with the information employees already have access to—but it can find and summarize that information in seconds.

Preparing your environment first ensures that only the right people have access to the right information.

How Microsoft Copilot Uses Your Data

One of the biggest misconceptions is that Microsoft Copilot trains on your company’s confidential data.

It does not.

Microsoft has stated that customer data remains within the Microsoft 365 tenant and is not used to train the public foundation models.

Instead, Copilot uses Microsoft Graph to access information users are already permitted to view.

That includes:

  • Outlook emails
  • Teams chats
  • SharePoint documents
  • OneDrive files
  • Calendar information
  • Word documents
  • Excel spreadsheets
  • PowerPoint presentations
  • Meeting transcripts

If an employee cannot normally access a document, Copilot cannot retrieve it for that employee.

This is why reviewing permissions before deployment is one of the most important steps.

Step 1: Audit Your Microsoft 365 Permissions

Before enabling Copilot, review how files and folders are shared across your organization.

Ask questions such as:

  • Are confidential HR folders accessible to everyone?
  • Does accounting data have restricted permissions?
  • Are executive documents protected?
  • Have former employees been removed?
  • Are external users still sharing files?
  • Are there “Everyone” permissions that should be eliminated?

Many organizations discover years of permission drift that occurred as employees changed roles or departments.

Cleaning these permissions improves security regardless of whether you implement Copilot.

Step 2: Classify Sensitive Data

Not every document should be treated the same.

Organizations should identify information such as:

  • Financial statements
  • Payroll records
  • Customer contracts
  • Medical information
  • Legal documents
  • Intellectual property
  • Employee records
  • Business strategies

Microsoft Purview sensitivity labels make it possible to classify and protect these files automatically.

Proper classification helps prevent accidental sharing and gives Copilot clear security boundaries.

Step 3: Enable Multi-Factor Authentication Everywhere

One compromised Microsoft 365 account can expose an entire organization.

Multi-factor authentication (MFA) dramatically reduces the likelihood of successful credential theft.

Before deploying AI, every privileged account—and ideally every employee account—should use MFA.

This simple control remains one of the most effective cybersecurity investments a business can make.

Step 4: Implement Conditional Access Policies

Employees don’t always work from the office anymore.

Many connect from home, airports, hotels, customer sites, or mobile devices.

Conditional Access allows organizations to control access based on:

  • User identity
  • Device compliance
  • Geographic location
  • Risk level
  • Application
  • Sign-in behavior

For example, a login attempt from another country may require additional verification or be blocked entirely.

These policies strengthen Microsoft 365 security before Copilot is introduced.

Step 5: Review External Sharing

SharePoint and OneDrive make collaboration easy, but they also increase the chance of oversharing.

Review:

  • Anonymous links
  • Guest accounts
  • Public folders
  • Expired sharing links
  • External collaborators

Removing unnecessary external access reduces security risks while ensuring Copilot only works with appropriately shared business information.

Step 6: Deploy Data Loss Prevention (DLP)

Data Loss Prevention policies help prevent sensitive information from leaving your organization.

Examples include blocking:

  • Social Security numbers
  • Credit card information
  • Financial records
  • Healthcare information
  • Confidential contracts

DLP policies continue protecting data whether employees share documents manually or use AI-assisted workflows.

Step 7: Train Your Employees

Technology alone cannot eliminate security risks.

Employees should understand:

  • What Copilot can do
  • What Copilot cannot do
  • Responsible AI usage
  • Data handling policies
  • Prompt best practices
  • Phishing awareness
  • Information classification

Well-trained users become one of the strongest security controls within an organization.

Common Mistakes Businesses Make

Organizations often encounter similar challenges when deploying AI.

Common mistakes include:

  • Enabling Copilot before reviewing permissions
  • Allowing excessive SharePoint access
  • Leaving inactive user accounts enabled
  • Failing to classify confidential documents
  • Ignoring guest accounts
  • Not enforcing MFA
  • Skipping employee training
  • Assuming AI creates new security risks instead of exposing existing ones

Avoiding these mistakes results in a much smoother deployment.

Why Work with a Microsoft 365 Partner?

Rolling out Microsoft Copilot isn’t just about purchasing licenses.

Successful deployments require:

  • Microsoft 365 security assessments
  • Permission reviews
  • Conditional Access configuration
  • Microsoft Defender optimization
  • Microsoft Purview implementation
  • Identity protection
  • Backup validation
  • Ongoing monitoring
  • Employee training

At Graphene Technologies, we help Houston businesses prepare their Microsoft 365 environments so they can adopt AI confidently while protecting their most valuable information.

Frequently Asked Questions

Is Microsoft Copilot secure?

Yes. Microsoft Copilot respects existing Microsoft 365 permissions and does not use your business data to train public AI models.

Can Copilot access confidential files?

Only if the user already has permission to access those files. Proper permission management is essential.

Does Copilot replace cybersecurity?

No. AI should complement—not replace—strong cybersecurity practices, identity protection, backup strategies, and employee training.

Should small businesses use Microsoft Copilot?

Absolutely. Small and midsize businesses can see significant productivity improvements when Copilot is implemented securely and managed correctly.

Final Thoughts

Microsoft Copilot has the potential to transform how businesses work, helping employees save time, make better decisions, and focus on higher-value tasks. But AI is only as secure as the Microsoft 365 environment behind it.

Before rolling out Copilot, take the time to review permissions, classify sensitive data, strengthen identity security, and establish clear governance. These steps not only protect your information but also ensure you get the maximum value from your AI investment.

If you’re ready to deploy Copilot with confidence, Graphene Technologies can help you assess your Microsoft 365 environment, improve security, and create a roadmap for a successful implementation.

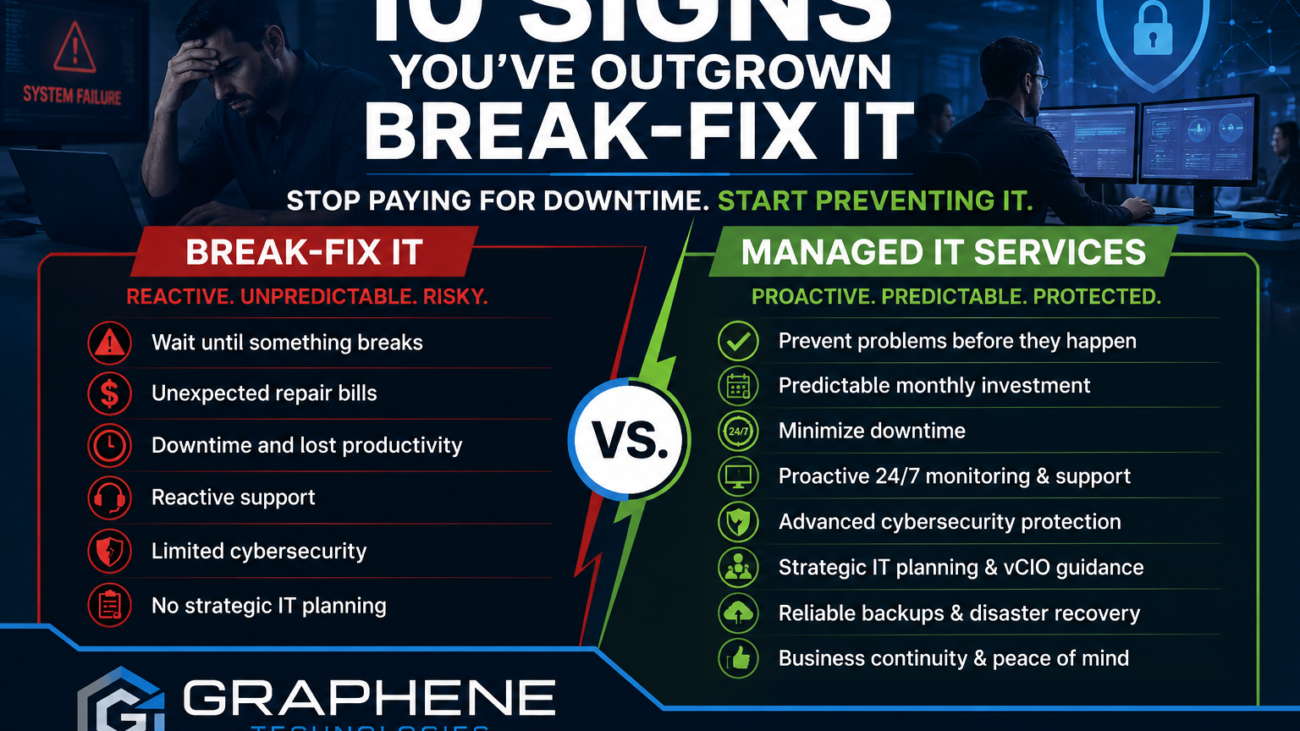
Comparison of break-fix IT versus managed IT services showing the benefits of proactive IT support, cybersecurity, and reduced downtime for Houston businesses.

10 Signs Your Business Has Outgrown Break-Fix IT | Managed IT Services Houston

If your company only calls an IT technician when something breaks, you’re using what’s known as the break-fix IT model. While this approach may seem less expensive at first, it often leads to unexpected downtime, cybersecurity risks, lost productivity, and higher long-term costs.

Today’s businesses depend on technology for nearly every aspect of their operations—from Microsoft 365 and cloud applications to cybersecurity, VoIP phone systems, remote work, and customer communication. Waiting until something fails is no longer a practical strategy.

That’s why more companies are switching to Managed IT Services Houston providers that proactively monitor, maintain, and secure their technology before problems disrupt the business.

At Graphene Technologies, we help Houston-area businesses move away from reactive IT support and toward a proactive technology strategy that improves reliability, security, and employee productivity.

If any of the following signs sound familiar, it may be time to consider managed IT services.

What Is Break-Fix IT?

Break-fix IT is exactly what it sounds like.

When a computer crashes, a server stops working, or employees cannot access email, you call an IT company to fix the issue. Once the problem is resolved, the technician leaves until the next emergency occurs.

Although this model was common years ago, it creates several problems:

  • No proactive maintenance
  • No ongoing cybersecurity monitoring
  • No technology planning
  • Unexpected repair bills
  • Higher downtime
  • Increased business risk

Modern businesses require continuous monitoring, patch management, endpoint protection, cloud security, backup verification, and strategic IT planning.

That is where a Managed Service Provider Houston businesses trust becomes valuable.

What Are Managed IT Services?

Managed IT Services provide your company with an outsourced IT department for a predictable monthly investment.

Instead of paying only when something breaks, your systems are monitored 24/7.

A managed IT provider handles:

  • Network monitoring
  • Microsoft 365 management
  • Windows updates
  • Patch management
  • Endpoint protection
  • Backup monitoring
  • Disaster recovery planning
  • User support
  • Cybersecurity
  • Strategic technology planning

Rather than waiting for problems, managed IT focuses on preventing them.

Sign #1 — You’re Calling IT More Often Than Ever

One of the biggest indicators you’ve outgrown break-fix support is increasing support requests.

Examples include:

  • Computers becoming slow
  • Wi-Fi constantly dropping
  • Printers failing
  • Outlook synchronization issues
  • Microsoft Teams problems
  • VPN failures
  • File sharing errors

Individually, these issues seem minor.

Collectively, they cost dozens—or even hundreds—of employee hours every year.

A proactive IT Support Houston provider identifies the root causes instead of repeatedly fixing symptoms.

Sign #2 — Downtime Is Becoming Expensive

Every hour your employees cannot work costs money.

Downtime affects:

  • Payroll
  • Customer service
  • Sales
  • Manufacturing
  • Accounting
  • Medical records
  • Project deadlines

According to multiple industry studies, downtime can cost small businesses thousands of dollars per hour when productivity, customer impact, and recovery efforts are considered.

Managed IT significantly reduces downtime through proactive monitoring, hardware lifecycle management, and continuous maintenance.

Instead of discovering a failing server after it crashes, monitoring tools alert technicians before the hardware fails.

Sign #3 — You’re Worried About Cybersecurity

Cybersecurity has changed dramatically over the last few years.

Small and midsize businesses are increasingly targeted because attackers know many organizations lack dedicated security staff.

Common threats include:

  • Ransomware
  • Phishing emails
  • Business Email Compromise (BEC)
  • Credential theft
  • Remote desktop attacks
  • AI-powered phishing
  • Data breaches

If your current IT provider only appears after an incident occurs, your business is already behind.

A modern Cybersecurity Services Houston provider should continuously monitor your environment, deploy endpoint detection and response (EDR), manage Microsoft 365 security, verify backups, and help your business implement security best practices before an incident occurs.

Sign #4 — Your Employees Keep Complaining About Technology

Employees rarely submit complaints unless technology is consistently slowing them down.

Common frustrations include:

  • Slow logins
  • Frozen computers
  • Shared drives disconnecting
  • Microsoft Teams issues
  • Wi-Fi dead zones
  • Email delays
  • Printer problems

Each issue may only waste five or ten minutes.

Multiply that across every employee, every day, and the hidden productivity loss becomes substantial.

Managed IT providers continuously optimize systems to eliminate recurring problems before employees notice them.

Sign #5 — Nobody Is Responsible for Your Technology Strategy

Many companies rely on an office manager or accountant to “handle IT.”

Unfortunately, those employees already have full-time jobs.

Without someone overseeing technology planning, businesses often experience:

  • Aging servers
  • Unsupported Windows versions
  • Expired warranties
  • Inconsistent backups
  • Weak cybersecurity policies
  • Unmanaged software licensing

Technology should support business growth—not become another operational headache.

A quality Managed IT Services Houston provider acts as your outsourced IT department and strategic technology advisor, helping you budget, plan, and modernize your environment.

Free Close-up of hands analyzing insurance policy paperwork with pen on table. Stock Photo

Immutable Backups Explained: What Houston Businesses Need to Know Before Renewing Cyber Insurance

Many business owners are surprised when they reach the cyber insurance section that asks:

“Do you maintain immutable, air-gapped, or offline backups of your critical business data?”

At first glance, the question seems straightforward. However, many organizations discover they do not know the answer.

Unfortunately, insurance carriers are asking this question for a reason.

Modern ransomware attacks frequently target backup systems before encrypting business data. As a result, organizations without protected backups often have no choice but to pay the ransom or permanently lose critical information.

According to guidance from the Cybersecurity and Infrastructure Security Agency (CISA), attackers commonly attempt to delete or disable backups before launching ransomware.

Therefore, cyber insurance companies increasingly require businesses to demonstrate that their backups cannot be altered or deleted by attackers.

If you’re unsure whether your current backup solution qualifies, this guide will help you understand what immutable backups are, what does not qualify, and how to verify your protection before signing your next cyber insurance application.

What Is an Immutable Backup?

An immutable backup is a backup that cannot be changed, deleted, or overwritten for a specific period of time.

Importantly, this protection applies even if an attacker gains administrative access to your systems.

In other words, neither:

  • Employees
  • IT administrators
  • Managed Service Providers (MSPs)
  • Cybercriminals

can modify or delete the backup during the defined retention period.

This protection is typically enforced at the storage level using technologies such as:

  • Object Lock
  • WORM (Write Once Read Many)
  • Immutable Storage
  • Retention Lock Policies

Although terminology varies by vendor, the objective remains the same.

The backup remains protected regardless of who has administrative access.

Because ransomware attackers often steal privileged credentials before launching an attack, immutable storage provides a critical last line of defense.

To learn more about ransomware protection, visit our Cybersecurity Services Houston page.

Three Common Backup Solutions That Do NOT Qualify

Many businesses believe they have immutable backups when they actually do not.

Let’s review the most common misconceptions.

1. A NAS Device or External Hard Drive

Many organizations store backups on:

  • NAS devices
  • External hard drives
  • Local storage appliances

Although these solutions provide redundancy, they do not provide immutability.

Because these devices remain connected to the network, ransomware can often reach them.

Furthermore, attackers who obtain administrative credentials may be able to delete the backup data entirely.

Therefore, a NAS or external drive alone generally does not satisfy cyber insurance requirements.

2. Microsoft 365 Retention Policies

Many businesses assume Microsoft automatically backs up everything inside Microsoft 365.

Unfortunately, that assumption is incorrect.

While Microsoft provides retention and recovery features, those features are not considered true backups for cyber insurance purposes.

Under Microsoft’s Shared Responsibility Model, customers remain responsible for protecting their own data.

Consequently, an attacker who gains Global Administrator access may still be able to delete data or remove retention controls.

For organizations relying heavily on Microsoft 365, we recommend reviewing our Microsoft 365 Consulting Services.

You can also review Microsoft’s official guidance here:

Microsoft Shared Responsibility Model

3. Cloud Backups Without Immutability Enabled

This is one of the most common issues we discover during cybersecurity assessments.

Many backup platforms support immutable storage. However, the feature is often disabled by default.

As a result, businesses assume they are protected when they are not.

Simply having a backup platform is not enough.

The immutability feature must be:

  • Enabled
  • Properly configured
  • Tested regularly
  • Protected by separate credentials

Without those controls, your backup may still be vulnerable to ransomware attacks.

Three Questions to Ask Your IT Provider Before Signing the Form

Before checking “Yes” on a cyber insurance application, ask your IT provider these three questions.

Question #1: Are Our Backups Immutable?

Ask:

“Are our backups immutable, and how long is the retention window?”

Many insurers now expect at least:

  • 14 days minimum
  • 30 days preferred
  • Longer retention for larger organizations

Because ransomware attackers may remain undetected for weeks, longer retention windows provide safer recovery options.

Question #2: Can Stolen Admin Credentials Delete Our Backups?

Ask:

“If our Microsoft 365 Global Admin account or Domain Admin account were compromised tomorrow, could an attacker delete our backups?”

The correct answer should be:

No.

If the answer is yes, your backups likely do not meet the intent of the insurance question.

Question #3: Can You Prove Immutability Is Enabled?

Ask for:

  • Screenshots
  • Vendor documentation
  • Configuration reports
  • Backup platform settings

A reputable provider should be able to provide documentation quickly.

If they cannot demonstrate immutability, assume it is not configured until proven otherwise.

What Does a Cyber Insurance-Compliant Backup Strategy Look Like?

A qualifying backup strategy includes several important elements.

Immutable Storage Enabled

First, the platform must have immutability actively configured.

Many leading platforms support immutable storage, including:

  • Veeam
  • Datto
  • Acronis
  • Rubrik
  • Microsoft Azure
  • Amazon S3 Object Lock

However, purchasing one of these products does not automatically guarantee compliance.

The configuration matters.

Isolated Backup Credentials

Next, backup administration should be separated from everyday business accounts.

For example, your Microsoft 365 Global Administrator account should not also control your backup platform.

Instead, organizations should use:

  • Dedicated backup administrator accounts
  • Separate authentication controls
  • Multi-Factor Authentication (MFA)

This separation significantly reduces risk.

Tested Recovery Procedures

Finally, backups must be tested.

A backup that has never been restored cannot be trusted during a disaster.

Many cyber insurance carriers now ask:

“When was your last successful restore test?”

Consequently, organizations should conduct periodic recovery testing and document the results.

To strengthen your disaster recovery posture, review our Managed IT Services Houston solutions.

What If Your Answer Is No?

Many businesses discover during renewal that they do not currently meet the requirement.

If that happens, be honest on the application.

Although a “No” answer may affect premiums, misrepresenting your environment can be far more costly.

Cyber insurance applications often function as warranty statements.

Therefore, if a post-breach investigation determines that your backups were not actually immutable, an insurance carrier may:

  • Deny the claim
  • Void the policy
  • Rescind coverage
  • Recover previous payouts

As a result, inaccurate responses can create substantial financial exposure.

Instead, use the renewal process as an opportunity to improve your security posture.

In many cases, enabling immutability is simply a configuration change rather than a major technology investment.

Why Immutable Backups Matter More Than Ever

Ransomware attacks continue to evolve.

Today, attackers focus on eliminating recovery options before encrypting systems.

Consequently, organizations can no longer assume traditional backups are enough.

Immutable backups provide a critical layer of protection because they prevent attackers from deleting the data needed for recovery.

For Houston businesses, this capability is increasingly becoming both a cybersecurity requirement and a cyber insurance requirement.

Schedule a Backup & Disaster Recovery Assessment

Not sure whether your backups meet cyber insurance requirements?

Graphene Technologies helps Houston businesses evaluate backup systems, disaster recovery plans, ransomware defenses, and cyber insurance readiness.

Our services include:

  • Backup & Disaster Recovery Assessments
  • Microsoft 365 Backup Solutions
  • Ransomware Protection Reviews
  • Cybersecurity Risk Assessments
  • Cloud Backup Design
  • Business Continuity Planning
  • Managed IT Services

Learn more:

  • Managed IT Services Houston
  • Cybersecurity Services Houston
  • Contact Graphene Technologies

Protect your data. Strengthen your cyber insurance position. Recover faster when incidents occur.

Free laptop computer keyboard vector

Passkey Migration: Why Houston Businesses Should Move Beyond Passwords

For decades, passwords have been the primary method of securing business accounts. However, they continue to be one of the weakest links in cybersecurity.

Employees reuse them. Attackers steal them. Help desks reset them.

As a result, businesses spend significant time and money managing a system that continues to fail.

Fortunately, there is a better alternative.

Passkey migration allows organizations to move away from traditional passwords and adopt phishing-resistant authentication. Instead of relying on shared secrets, passkeys use the built-in security features already available on modern devices.

Because passkeys improve security while simplifying the login experience, more businesses are making the transition every year.

Why Passwords Continue to Create Security Risks

Despite decades of security improvements, passwords remain a leading cause of data breaches.

According to the Verizon Data Breach Investigations Report (DBIR), compromised credentials are involved in more than 80% of successful breaches.

The problem is simple.

Passwords are shared secrets. Therefore, they must be stored somewhere. Eventually, stolen credentials appear in phishing campaigns, malware infections, data breaches, or credential stuffing attacks.

Although Multi-Factor Authentication (MFA) significantly improves security, not all MFA methods provide the same level of protection.

For example, SMS-based authentication remains vulnerable to:

  • Phishing attacks
  • SIM swapping
  • Social engineering
  • Session hijacking

Consequently, cybersecurity experts increasingly recommend phishing-resistant authentication methods.

To learn more about protecting your business from modern cyber threats, visit our Cybersecurity Services Houston page.

What Is a Passkey?

A passkey is a secure digital credential that replaces traditional passwords.

Rather than storing a password on a server, passkeys use cryptographic key pairs.

When a user registers with a service:

  • A private key is stored securely on their device.
  • A public key is stored by the service provider.

Later, when the user signs in, the device verifies their identity using:

  • Face ID
  • Fingerprint authentication
  • Windows Hello
  • Device PIN

Because the private key never leaves the device, attackers cannot steal it through phishing websites or server breaches.

Additionally, passkeys are tied directly to legitimate websites. Therefore, fake login pages cannot trick users into authenticating.

This makes passkeys one of the most effective defenses against account compromise.

Why Passkeys Are More Secure Than Passwords

Traditional passwords create several security challenges.

For example:

  • Users forget them.
  • Employees reuse them.
  • Attackers steal them.
  • Help desks constantly reset them.

Passkeys eliminate many of these problems.

Unlike passwords, passkeys:

  • Cannot be reused across sites
  • Cannot be guessed
  • Cannot be phished
  • Cannot be stolen from a breached database
  • Do not require users to memorize anything

As a result, passkeys provide both stronger security and a better user experience.

The technology is based on the FIDO2 and WebAuthn standards supported by Microsoft, Google, and Apple.

According to the FIDO Alliance, billions of online accounts now support passkey authentication, and adoption continues to accelerate worldwide.

What Does Passkey Migration Actually Mean?

Many business owners assume passkey migration requires a complete technology overhaul.

Fortunately, that is not the case.

In reality, passkey migration is typically a gradual process.

Most organizations run passwords and passkeys side-by-side during the transition period.

This approach allows users to become familiar with passkeys while maintaining access to existing systems.

A typical migration plan includes:

  • Identifying applications that already support passkeys
  • Selecting pilot users
  • Creating fallback authentication options
  • Developing user training materials

Because Microsoft and Google already support passkeys, many businesses can begin the process immediately.

Microsoft 365 and Passkeys

Microsoft has aggressively expanded passkey support through Microsoft Entra ID.

Organizations using Microsoft 365 Business Premium, Microsoft 365 E3, or Microsoft 365 E5 can leverage passkey authentication today.

If your organization uses Microsoft 365, we recommend reviewing our Microsoft 365 Consulting Services for implementation guidance.

How Houston Businesses Should Approach Passkey Migration

Start With High-Risk Users

Rather than deploying passkeys to everyone at once, begin with:

  • Administrators
  • Executives
  • Finance teams
  • IT staff
  • Power users

These users often have elevated privileges and represent attractive targets for attackers.

Additionally, their feedback can help refine the rollout before expanding to the broader organization.

Run Passwords and Passkeys Together

Many organizations make the mistake of treating migration as an immediate cutover.

Instead, passwords and passkeys should operate together during the transition period.

This approach minimizes disruptions while allowing employees to enroll devices gradually.

As a result, organizations avoid unnecessary support tickets and user frustration.

Address Legacy Applications

Although passkey adoption is growing rapidly, some business applications still rely on traditional passwords.

For these systems, password managers remain an excellent interim solution.

Organizations should enforce:

  • Unique passwords
  • Secure password storage
  • MFA protection
  • Regular credential reviews

Eventually, as vendors add passkey support, migration becomes significantly easier.

The Business Benefits Extend Beyond Security

Improved security is the primary reason businesses adopt passkeys.

However, operational benefits are equally compelling.

According to research published by Google, passkey sign-ins are substantially more successful than password-based authentication.

As a result, businesses experience:

  • Fewer failed login attempts
  • Reduced password reset requests
  • Improved user productivity
  • Lower help desk costs
  • Faster authentication

Furthermore, employees spend less time dealing with passwords and more time focusing on their work.

For many organizations, this productivity gain alone justifies the investment.

Compliance and Regulatory Advantages

Security regulations continue to evolve.

Consequently, organizations must adopt stronger authentication methods to meet modern compliance requirements.

The NIST Digital Identity Guidelines (SP 800-63-4) emphasize phishing-resistant authentication for higher-assurance environments.

Therefore, passkey adoption can support compliance initiatives related to:

  • Cyber insurance requirements
  • Regulatory audits
  • Risk management programs
  • Security frameworks
  • Zero Trust strategies

Businesses planning future compliance initiatives should consider passkeys as part of their broader security roadmap.

Moving Toward a Passwordless Future

Passwords are not disappearing overnight.

Nevertheless, the industry is clearly moving toward passwordless authentication.

Organizations that begin planning now will improve security, reduce support costs, and create a better experience for employees.

At Graphene Technologies, we help Houston businesses modernize authentication through:

  • Managed IT Services
  • Microsoft 365 Security Reviews
  • Microsoft Entra ID Configuration
  • Cybersecurity Assessments
  • Conditional Access Policies
  • Multi-Factor Authentication Deployment
  • Passkey Migration Planning
  • Zero Trust Security Initiatives

To learn more about our services, visit:

  • Managed IT Services Houston
  • Cybersecurity Services Houston
  • Microsoft 365 Consulting

Schedule a Passkey Readiness Assessment

Not sure whether your organization is ready for passkeys?

Graphene Technologies can assess your Microsoft 365 environment, identity platform, authentication policies, and application ecosystem to build a practical migration roadmap.

Contact us today at and discover how a passwordless future can strengthen your security posture while simplifying the user experience.