AI phishing attacks targeting Houston businesses

AI Phishing Attacks: What Houston Businesses Need to Know

Yes. This one has good material, but I would reposition it around a stronger search phrase such as “AI phishing attacks” + “Houston businesses” and make the article lead naturally into Graphene’s cybersecurity services.

I also checked the underlying claims. The NCSC does specifically say generative AI can create convincing phishing lures without the translation, spelling, and grammatical mistakes that historically exposed them. The FBI likewise warns that criminals use generative AI to create believable spear-phishing and financial-fraud messages and reduce grammatical/spelling errors. National Cyber Security Centre

One correction: the 22,364 complaints / $893 million figure comes from the FBI’s 2025 IC3 report, not the older FBI alert linked in the original article. The 2025 report says AI-related information was reported in 22,364 complaints with adjusted losses exceeding $893 million. Internet Crime Complaint Center

Here is the version I’d publish.

AI Phishing Attacks: What Houston Businesses Need to Know

For years, one of the easiest ways to spot a phishing email was bad spelling.

Strange grammar, awkward sentences and obvious mistakes could quickly signal that an email claiming to be from your bank, supplier or CEO wasn’t legitimate.

AI is changing that.

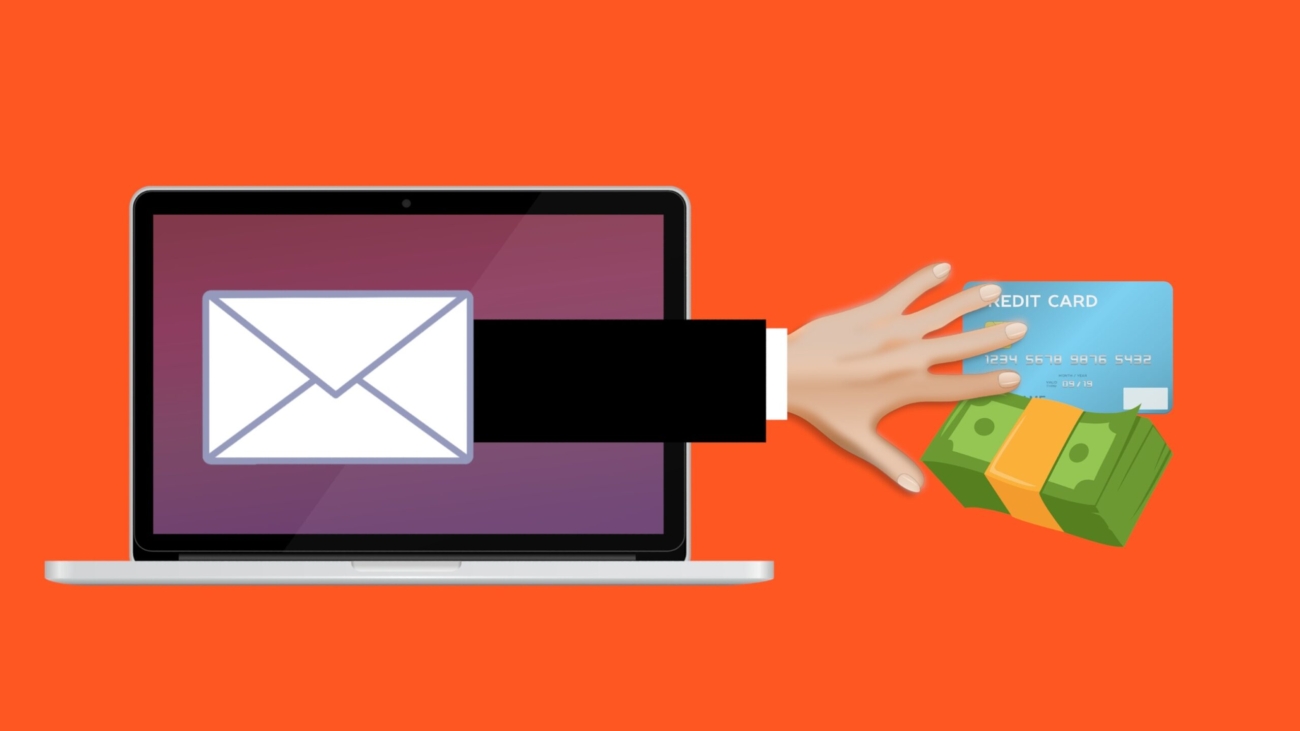
Cybercriminals can now use generative AI to produce polished, professional-looking phishing emails in seconds. Messages can be personalized, grammatically correct and written in a tone that looks surprisingly similar to legitimate business communication.

For Houston businesses, that means employee phishing training needs to change too.

Instead of asking only, “Does this email look fake?”, employees increasingly need to ask:

“What is this email asking me to do?”

How AI Is Making Phishing Emails Harder to Spot

The UK’s National Cyber Security Centre (NCSC) has warned that generative AI can create convincing phishing material without many of the translation, spelling and grammatical errors that traditionally exposed phishing attempts. National Cyber Security Centre

The FBI has issued a similar warning.

According to the FBI, criminals are using generative AI to create believable content for social engineering, spear phishing and financial fraud. AI also allows criminals to produce messages faster, improve translations and eliminate language mistakes that might otherwise alert the recipient. Internet Crime Complaint Center

That changes what a modern phishing email can look like.

Instead of:

“Dear Customer, Your Account Have Been Suspended.”

an employee might receive a polished email that appears to come from a real supplier, references a plausible business situation and asks the accounting department to update payment information.

The writing may be perfect.

The request is the warning sign.

Why AI Phishing Can Be So Convincing

AI gives attackers several advantages.

The Writing Looks Professional

Generative AI can produce grammatically correct business emails in almost any tone.

An attacker no longer needs strong English-language skills to create a convincing email targeting a U.S. company.

Messages Can Be Personalized

Information about many businesses and employees is publicly available.

Company websites, LinkedIn profiles, press releases and social media can reveal employee names, job titles, suppliers, executives, projects and organizational relationships.

That information can potentially be incorporated into targeted social-engineering messages.

A finance employee could receive something that appears to be from an executive. A purchasing employee could receive what looks like a supplier request. An HR employee could receive a message appearing to come from another employee.

This type of targeted phishing is commonly called spear phishing.

Attackers Can Produce More Messages

AI also reduces the time required to create believable content.

The FBI says generative AI allows criminals to create messages faster and reach wider audiences with believable content. Internet Crime Complaint Center

The scale of AI-assisted fraud is already significant. The FBI’s 2025 Internet Crime Report recorded 22,364 complaints reporting AI-related information and more than $893 million in adjusted losses. Those figures cover AI-related cybercrime broadly rather than phishing alone, but they illustrate how AI has become part of the fraud landscape. Internet Crime Complaint Center

AI Phishing Isn’t Just an Email Problem

Generative AI can also be used for voice cloning, images and video.

The FBI warns that criminals can use AI-generated audio to impersonate relatives and other people, including creating audio that requests emergency financial assistance. It also describes AI-generated video being used to impersonate company executives and other authority figures. Internet Crime Complaint Center

For businesses, imagine receiving an urgent voicemail that appears to be from an executive:

“I need this wire processed before the end of the day. I’m heading into a meeting, so please handle it immediately.”

Recognizing the person’s voice should no longer be enough to override your company’s verification procedures.

Can Your Spam Filter Stop AI Phishing?

Modern email security remains an important part of protecting a business, but businesses shouldn’t assume that every fraudulent message will automatically be blocked.

A targeted social-engineering email doesn’t necessarily need malware or an obviously malicious attachment.

It could simply ask an employee to:

change payment instructions, send confidential information, log into an account, purchase gift cards, or call a fraudulent telephone number.

That’s why cybersecurity needs multiple layers: email security, identity protection, MFA, employee awareness and documented verification procedures.

7 Warning Signs Employees Should Look for Now

Perfect spelling doesn’t make an email trustworthy.

Teach employees to pay particular attention when a message:

  1. Requests money or a wire transfer.
  2. Changes supplier or customer bank information.
  3. Asks for a password, MFA code or other credential.
  4. Creates unusual urgency or pressure.
  5. Contains an unexpected attachment or link.
  6. Uses a familiar display name but an unfamiliar email address.
  7. Asks the employee to bypass a normal business procedure.

These signals focus on behavior and intent rather than grammar.

That distinction is increasingly important as AI-generated messages become more convincing.

How Houston Businesses Can Reduce AI Phishing Risk

Technology should be combined with clear procedures employees can actually follow.

Verify Payment Changes Outside Email

Create a simple rule:

Any request to change banking or payment information must be independently verified.

Call the supplier using a telephone number your company already has on record.

Don’t use the telephone number contained in the email requesting the change.

Use Phishing-Resistant MFA

MFA provides another layer of protection if an employee’s password is compromised.

But not all MFA methods provide the same protection.

CISA recommends businesses move toward phishing-resistant MFA and identifies security keys as offering particularly strong protection. CISA also recommends requiring MFA for systems such as email, file storage and remote access. CISA

For organizations using Microsoft 365, identity and MFA configuration should be an important part of the company’s overall Microsoft 365 security strategy.

Train Employees for Modern Phishing

Stop making bad grammar the centerpiece of phishing training.

Instead, teach employees to recognize:

unexpected requests + urgency + money + credentials + changes in normal procedure.

Give employees an easy way to report suspicious messages.

The objective isn’t to turn every employee into a cybersecurity expert. It’s to establish a predictable response when something unusual occurs.

Protect High-Risk Employees More Aggressively

Not every employee has the same risk.

Pay particular attention to accounts belonging to:

  • Owners and executives
  • Accounting and finance
  • HR
  • IT administrators
  • Employees authorized to make payments
  • Employees with access to sensitive customer information

A compromised accounting mailbox can have very different consequences from a compromised low-privilege account.

Create a Payment Verification Procedure

Technology can’t replace a good business process.

For example:

Email requests bank change → Employee calls known supplier contact → Change independently verified → Payment information updated

An “urgent” email from an executive shouldn’t bypass that process.

AI makes this procedure more important, not less.

What If an Employee Clicks a Phishing Link?

Speed matters.

Employees should immediately report the incident rather than trying to hide the mistake.

Depending on what occurred, your IT team may need to:

  • Reset the employee’s password
  • Revoke active sessions
  • Review sign-in activity
  • Investigate mailbox rules
  • Check for unauthorized account changes
  • Determine whether sensitive information was accessed
  • Review affected endpoints
  • Investigate other employees who received the same message

The earlier your IT provider knows about a suspected compromise, the sooner it can investigate and contain it.

Frequently Asked Questions

Can You Still Spot Phishing by Bad Spelling?

Sometimes, but it is no longer a reliable test.

The NCSC specifically warns that generative AI can produce phishing material without many of the spelling, grammatical and translation mistakes historically associated with phishing. National Cyber Security Centre

What Are the Biggest Phishing Warning Signs Today?

Focus on what the sender wants you to do.

Requests involving money, changed banking information, passwords, MFA codes, confidential information or unusual urgency deserve additional verification.

Also check the sender’s actual email address rather than relying solely on the displayed name.

Can AI Clone Someone’s Voice?

AI can generate audio that imitates another person. The FBI has warned that criminals use AI-generated audio to impersonate people and solicit payments. Internet Crime Complaint Center

Treat an unexpected voice request involving money or sensitive information the same way you would a suspicious email: independently verify it through a trusted channel.

Will Microsoft 365 Stop Every Phishing Email?

No security platform should be treated as a guarantee that every phishing message will be blocked.

Businesses should combine properly configured email security with MFA, identity controls, employee awareness, endpoint protection and procedures for sensitive financial requests.

Is MFA Enough to Stop Phishing?

MFA significantly strengthens account security, but the type of MFA matters.

CISA recommends moving toward phishing-resistant MFA and notes that traditional methods such as text/email codes provide weaker protection than stronger alternatives. CISA

Is Your Houston Business Prepared for AI Phishing?

AI has changed what a fraudulent email can look and sound like.

Your cybersecurity strategy needs to change with it.

Graphene Technologies helps Houston businesses protect Microsoft 365, email, endpoints, identities and company data against modern cybersecurity threats.

If you’re unsure whether your current email and Microsoft 365 security settings are properly configured, we’ll help you identify the gaps.

Schedule a Free 30-Minute IT Assessment

We’ll review your current IT and cybersecurity environment and identify areas that may leave your business exposed to phishing, account compromise and other threats.
BYOD security for Houston businesses

BYOD Security for Houston Businesses: How to Protect Company Data on Personal Devices

Employees using personal phones and laptops for work has become normal for many small and midsize businesses. An employee may add Microsoft 365 email to an iPhone, access company files from a home computer, join Teams meetings from a tablet, or download customer information to a personal laptop.

The convenience is obvious. The security risk is often less visible.

Once company information reaches a personal device, your business has less control over where that information is stored, which applications can access it, whether the device is properly updated, and what happens to the data if the employee leaves.

For Houston businesses using a Bring Your Own Device (BYOD) policy, the answer isn’t necessarily banning personal devices. The better approach is deciding what employees can access, which devices are permitted, and what security controls must be in place.

What Is BYOD?

BYOD stands for Bring Your Own Device. It refers to employees or contractors using personally owned phones, tablets, or computers for business.

That might include:

  • Accessing Microsoft 365 or Google Workspace
  • Adding company email to a personal phone
  • Opening customer or company documents
  • Using Teams, Zoom, Slack, or other business applications
  • Accessing CRM or accounting systems
  • Downloading files to a personal computer
  • Connecting to company cloud applications

The security issue isn’t simply who owns the device. It’s where your company’s data goes once that device is allowed access.

Why BYOD Can Create Security Risks for Houston Businesses

On a company-owned computer, your IT provider can control security settings, software, updates, encryption and access.

A personal device is different.

Employees may determine which applications are installed, when updates are performed, where files are backed up and whether other family members use the device. Even when management software is deployed, the level of control varies depending on the operating system and enrollment method. Pasted text

For a Houston SMB, several problems deserve particular attention.


1. Business Files Can End Up in Personal Storage

An employee downloads a customer spreadsheet from Microsoft 365.

Now that file might exist in:

Microsoft 365 → Downloads folder → personal cloud backup

Opening it in another application can create additional unmanaged copies.

Disabling the employee’s Microsoft 365 account later doesn’t necessarily remove those copies.

2. Personal Devices May Not Be Properly Updated

Your IT team may have limited visibility into whether an employee’s personal laptop is running a supported operating system or has current security patches.

An outdated personal computer accessing company email or cloud applications can introduce unnecessary risk.

3. Family Members May Share the Device

Home computers are frequently shared.

If an employee uses the same Windows or macOS account as a spouse or child, company files, saved browser sessions and other business information may become accessible to another person.

A BYOD policy should require separate user accounts and prevent access from devices where business information cannot be adequately separated from other users.

4. Personal Apps Can Interact With Business Information

Employees decide what software gets installed on their personal devices.

Some applications may have access to files, contacts, browser information or clipboard contents.

Without appropriate controls, your company may have little visibility into what happens to business information after it reaches that device.

5. Employee Offboarding Becomes More Complicated

Suppose an employee leaves your Houston business tomorrow.

Your IT provider can disable the employee’s Microsoft 365 account and revoke active sessions.

But what about files already downloaded to their personal laptop?

That is one of the biggest reasons businesses should establish BYOD controls before allowing employees to use personal devices.

7 BYOD Security Controls Houston Businesses Should Consider

A good BYOD strategy combines account security, device security and data protection.

1. Require Multi-Factor Authentication

MFA should be required for Microsoft 365, cloud storage and other important business applications.

MFA helps protect the user’s account if a password is compromised, but it doesn’t solve every BYOD problem.

A downloaded customer file, for example, still needs appropriate device and data protection.

2. Require Supported Operating Systems

Devices accessing company resources should run operating systems that still receive security updates.

Older devices that can no longer receive current security patches should not be allowed to access company information.

3. Require Device Encryption

Full-device encryption helps protect information stored on a laptop or phone if the device is lost or stolen.

Encryption should be enabled before the device disappears—not after an incident occurs.

4. Require Screen Locks

Require employees to protect devices with a strong PIN, password, fingerprint or facial recognition and configure automatic screen locking.

It’s a simple control, but an important one.

5. Use Approved Business Applications

Define which applications employees may use for:

email, messaging, file sharing, cloud storage, remote access and other company work.

Where possible, prevent company information from being copied into unmanaged applications or personal storage.

6. Consider Microsoft Intune and Application Management

For organizations using Microsoft 365, Microsoft Intune can help manage devices and protect company information.

Mobile Device Management (MDM) can apply policies to enrolled devices and determine whether they meet company security requirements.

Mobile Application Management (MAM) can protect information inside supported business applications without necessarily managing the employee’s entire personal device.

Depending on configuration, businesses can restrict copying, prevent saving information to personal locations and remove company information from managed applications when an employee leaves. The existing draft correctly distinguishes selective removal of managed company data from a full factory reset. Pasted text

7. Have a Lost-Device and Offboarding Process

Employees should know exactly who to contact when a device is:

lost, stolen, infected, replaced, repaired or sold.

Your IT team can then take appropriate steps such as revoking sessions, disabling access, removing managed company information and reviewing account activity.

The same process should be part of employee offboarding.

When Should Houston Businesses NOT Allow BYOD?

Personal devices aren’t appropriate for every employee or every type of work.

A company-owned, managed device is generally preferable when an employee:

  • Handles sensitive or regulated information
  • Has administrator privileges
  • Manages user accounts or security systems
  • Needs large amounts of company information stored locally
  • Shares the personal device with other people
  • Uses an unsupported operating system
  • Cannot enable encryption
  • Cannot keep company information separated from personal information

This is particularly important for administrators. Someone responsible for Microsoft 365 administration, backups, security settings or other critical business systems should perform that work from a managed company device, not an unmanaged home computer. Pasted text

What Should a BYOD Policy Include?

Your written BYOD policy should establish who can use personal devices, which devices are acceptable, what applications employees must use, whether files can be downloaded, required security settings, what your IT provider can manage, what happens when a device is lost, and how company information is removed when employment ends.

Employees should understand and accept these requirements before business access is provided. Pasted text

Is MFA Enough for BYOD Security?

No.

MFA protects the employee’s account. It doesn’t automatically protect information downloaded onto the device.

A more complete BYOD security strategy may include:

MFA + encryption + security updates + approved applications + access policies + MDM/MAM + documented offboarding procedures.

The appropriate combination depends on what information employees access and how they work.

Need Help Securing Personal Devices in Your Houston Business?

If employees are already checking company email, opening files or accessing Microsoft 365 from personal devices, you may already have a BYOD environment—even if your company has never formally created a BYOD policy.

Graphene Technologies helps Houston businesses secure Microsoft 365, endpoints, cloud applications and employee access.

We can review your current environment, identify where personal devices have access to company information, and recommend practical security controls without unnecessarily disrupting how your employees work.

Not sure whether your current setup is secure?

Schedule a Free 30-Minute IT Assessment

We’ll review your current IT and security environment and help identify areas that deserve attention.


Business website cybersecurity and protection concept for a Houston small business

Is Your Business Website a Security Risk? A Houston SMB Guide

Your website can become an overlooked security problem

A business website may run for months without anyone checking its security. However, websites need maintenance just like other technology.

Plugins become outdated. Administrator accounts remain active. In addition, backups may stop working without anyone noticing.

Attackers often scan many websites automatically. Therefore, they do not need to target your business by name to find a weakness.

Keep WordPress, plugins, and themes updated

WordPress sites depend on several software components. Each component can receive security updates.

Therefore, businesses should apply supported updates promptly. Delaying updates can leave a known weakness exposed.

However, do not update blindly on a critical website. Maintain a backup and test major changes when possible. That approach improves both security and reliability.

Protect administrator accounts

Website administrator accounts deserve strong protection because they can change the entire site.

First, give each administrator a separate account. Next, remove old developers, employees, and vendors who no longer need access.

Also, use strong unique passwords and MFA when available. Most importantly, avoid sharing one administrator password among several people.

Review forms and connected services

Contact forms often collect customer information. Some websites also connect to payment systems, email marketing platforms, or other business applications.

Therefore, review what information each form collects. Keep only what the business actually needs.

In addition, protect the accounts connected to those services. A secure website can still create risk if an integrated account has weak access controls.

Maintain a recovery plan

A website backup gives the business a way to recover after a bad update or security incident. However, a backup is useful only if it works.

Keep recent copies and understand how to restore them. Also, know who is responsible for the recovery process.

If an outside web developer manages the site, document that relationship. Your business should still know where the domain, hosting, DNS, and backups are managed.

Watch for signs of compromise

A hacked website does not always go offline. Instead, attackers may add hidden pages, redirects, spam, or malicious code.

Therefore, investigate unexpected website changes quickly. Also, pay attention to browser warnings and unusual search results.

Graphene Technologies helps Houston businesses review the security around websites, domains, DNS, accounts, backups, and connected systems. Schedule a free 30-minute IT assessment to identify technology and cybersecurity risks before they become larger problems.

Call to Action

Need a clearer picture of your IT risks and priorities? Schedule a Free 30-Minute IT Assessment with Graphene Technologies. We will review your current environment and identify practical next steps.

Cybersecurity illustration featuring a security shield, cloud protection, laptop, and secure network infrastructure representing proactive cybersecurity services for businesses.

The 2026 Cybersecurity Checklist Every Houston Business Should Complete

Cyber threats continue to evolve, and businesses of every size are being targeted. Fortunately, organizations can reduce their exposure by following proven security practices. In this guide, you’ll find ten practical steps that improve security, reduce downtime, and strengthen business resilience. Moreover, each recommendation is designed for small and midsize businesses that rely on Microsoft 365 and cloud technology.

1. Enable Multi-Factor Authentication

First, require multi-factor authentication (MFA) for every employee. In addition, protect administrator accounts with stronger authentication methods. As a result, stolen passwords become much less valuable to attackers.

2. Keep Systems Updated

Next, install security updates for Windows, Microsoft 365 Apps, servers, browsers, and network equipment. Although updates can be inconvenient, they close known vulnerabilities before criminals exploit them.

3. Secure Microsoft 365

Review Conditional Access, Microsoft Defender, mailbox forwarding rules, external sharing, and legacy authentication. Furthermore, disable unused accounts and verify that privileged users follow stricter security policies.

4. Review User Permissions

Employees often change responsibilities over time. Therefore, review permissions for SharePoint, OneDrive, HR folders, finance systems, and network shares. Finally, remove unnecessary access by following the principle of least privilege.

5. Verify Your Backups

Backups are only valuable if they work. For that reason, test file restores and server recovery regularly. Likewise, maintain an immutable or offline backup copy to improve ransomware recovery.

6. Protect Every Endpoint

Deploy endpoint detection and response, encryption, and business-grade firewall protection. In addition, replace unsupported devices before they become a security risk.

7. Train Employees

Technology alone cannot stop every attack. Instead, provide ongoing security awareness training. For example, teach employees how to recognize phishing emails, fake invoices, QR-code scams, and suspicious links.

8. Strengthen Network

Secure wireless networks with strong encryption and separate guest traffic from business traffic. Meanwhile, monitor network activity to identify unusual behavior before it becomes a larger problem.

9. Monitor Continuously

Continuous monitoring improves visibility across your environment. Consequently, your IT team can detect malware, failed logins, and suspicious activity much faster.

10. Create an Incident Response Plan

Finally, document who to contact, how to isolate affected devices, how to restore backups, and how to communicate with employees and customers. Above all, practice the plan before an emergency occurs.

Cybersecurity Checklist

  • Enable MFA for all users
  • Apply software updates promptly
  • Review Microsoft 365 security settings
  • Audit user permissions
  • Test backup recovery
  • Deploy endpoint protection
  • Train employees regularly
  • Secure network infrastructure
  • Monitor systems continuously
  • Maintain an incident response plan

Conclusion

Overall, cybersecurity is an ongoing process rather than a one-time project. By completing this checklist, businesses can significantly reduce their cyber risk. Furthermore, proactive security lowers downtime, protects customer trust, and supports long-term growth. If your organization needs help implementing these recommendations, Graphene Technologies can provide managed cybersecurity, Microsoft 365 security, and proactive IT support throughout the Houston area.

Free hacker computer programming vector

The Hidden Cybersecurity Risk Most Houston Businesses Overlook: Personal Web Habits

When business owners think about cybersecurity threats, they often picture ransomware attacks, sophisticated hackers, or advanced malware. However, most successful cyberattacks begin much closer to home.

In fact, many breaches start with everyday actions such as checking a personal email account, reusing a password, or uploading a file to an unapproved cloud service because it feels more convenient.

According to the Verizon Data Breach Investigations Report (DBIR), 68% of data breaches involve a human element. Therefore, businesses can no longer focus solely on technology when developing a cybersecurity strategy.

Today, employees work across multiple devices, cloud applications, and remote locations. As a result, the line between personal and business activity continues to blur. Understanding where that overlap creates risk is essential for every organization.

The Security Gap Outside Traditional IT Controls

Most employees are not intentionally putting company data at risk. Instead, they are simply trying to work efficiently.

For example, employees may:

  • Check personal email on a company laptop
  • Save passwords in a web browser
  • Upload files to personal cloud storage
  • Access social media during breaks
  • Use AI tools to speed up routine tasks

Individually, these actions appear harmless. However, they often create pathways that bypass traditional security controls.

While firewalls, antivirus software, and endpoint protection remain important, they cannot fully protect data when users move information outside approved systems.

Consequently, businesses must address both technical vulnerabilities and human behavior.

Why Cybercriminals Prefer Personal Channels

Personal Email and Social Media Are Prime Targets

Cybercriminals understand that personal email accounts and social media platforms typically have fewer protections than corporate systems.

As a result, attackers frequently use:

  • Fake package delivery notifications
  • Fraudulent banking alerts
  • Social media messages
  • Streaming subscription scams
  • Password reset requests

Furthermore, these attacks often create a sense of urgency. Employees who are busy or distracted may click before verifying the source.

Once that happens, the attacker can gain access to credentials, install malware, or redirect the user to a malicious website.

Because personal and business activities frequently occur on the same device, a single click can expose corporate systems.

For additional protection strategies, read our Cybersecurity Services for Houston Businesses page.

You can also review the latest findings from the Verizon Data Breach Investigations Report.

Password Reuse Turns Personal Breaches Into Business Incidents

Password reuse remains one of the most common cybersecurity risks.

Unfortunately, many people continue to use similar passwords across personal and business accounts. Consequently, a breach involving a personal account can quickly become a business problem.

Cybercriminals routinely perform credential stuffing attacks. In these attacks, stolen usernames and passwords are automatically tested against business systems such as:

  • Microsoft 365
  • VPN portals
  • Remote Desktop services
  • Cloud applications
  • Business email accounts

Fortunately, organizations can significantly reduce this risk.

Recommended Security Controls

Businesses should implement:

  • Multi-Factor Authentication (MFA)
  • Password managers
  • Microsoft Entra ID security policies
  • Conditional Access controls

Moreover, these controls help prevent attackers from accessing business accounts even when passwords have already been compromised.

Learn more about our Microsoft 365 Consulting Services.

Additionally, the Cybersecurity and Infrastructure Security Agency (CISA) recommends MFA as one of the most effective security measures available.

Shadow IT: The Growing Security Challenge

Many employees use unauthorized applications without realizing the security implications.

This practice, commonly known as Shadow IT, usually begins with convenience rather than malicious intent.

For instance, employees may use:

  • Personal Dropbox accounts
  • Google Drive
  • Consumer messaging applications
  • Public AI tools
  • Personal file-sharing platforms

Initially, these tools may improve productivity. However, they also create visibility and compliance challenges.

Once company data leaves approved systems, IT teams can no longer:

  • Monitor activity
  • Apply retention policies
  • Track data access
  • Conduct audits
  • Enforce security controls

Therefore, even well-intentioned employees can unintentionally increase organizational risk.

To learn how proactive management can reduce these risks, visit our Managed IT Services Houston page.

Why Blocking Everything Rarely Works

Many organizations attempt to solve security concerns through restrictions.

Although this approach appears logical, it often produces unintended consequences.

When businesses block applications or websites without providing alternatives, employees typically find workarounds. As a result, activity moves outside managed environments where IT teams lose visibility.

Consequently, the risk does not disappear. Instead, it becomes harder to monitor and manage.

Modern cybersecurity strategies focus on risk reduction rather than perfect compliance. Therefore, organizations should prioritize visibility, education, and secure alternatives.

What Actually Reduces Cybersecurity Risk?

Create Separation Between Personal and Business Activities

One of the simplest and most effective security improvements involves separating personal and professional activity.

For example, businesses can encourage:

  • Separate browser profiles
  • Dedicated work devices
  • Company-managed identities
  • Secure cloud applications
  • Mobile device management policies

As a result, a compromise in a personal account is less likely to affect business systems.

Assume Passwords Will Eventually Be Exposed

No organization can completely eliminate credential theft.

Therefore, security programs should be designed around the assumption that passwords will eventually be compromised.

Businesses should deploy:

  • Multi-Factor Authentication
  • Conditional Access Policies
  • Password Managers
  • Endpoint Detection and Response (EDR)
  • Risk-Based Authentication

Together, these controls significantly reduce the likelihood of a successful attack.

For businesses seeking a stronger security posture, our Cybersecurity Services team can help evaluate existing controls.

Make Secure Choices the Easy Choices

The most effective cybersecurity programs make secure behavior simple.

Employees are far more likely to follow security policies when approved tools are:

  • Easy to access
  • Fast to use
  • Reliable
  • Well supported

Consequently, organizations should focus on enabling productivity while maintaining security.

Rather than fighting user behavior, successful businesses design systems that support how employees actually work.

How Houston Businesses Can Reduce Human-Driven Cybersecurity Risk

Human behavior will always play a role in cybersecurity. Nevertheless, businesses can dramatically reduce risk by implementing the right controls, training, and technologies.

At Graphene Technologies, we help Houston businesses strengthen their cybersecurity posture through:

  • Managed IT Services
  • Microsoft 365 Security Reviews
  • Security Awareness Training
  • Endpoint Detection and Response (EDR)
  • Microsoft Entra ID Security Configuration
  • Compliance Assessments
  • Cloud Security Solutions
  • Cybersecurity Risk Assessments

Because every organization faces different challenges, we tailor our recommendations to your business goals, compliance requirements, and risk profile.

Schedule a Cybersecurity Assessment

If you’re unsure whether personal web habits are creating security gaps within your organization, now is the time to find out.

Graphene Technologies can perform a comprehensive cybersecurity assessment of your Microsoft 365 environment, cloud infrastructure, user security practices, and endpoint protection systems.

Contact us today to schedule your assessment.

Protect your business. Strengthen your security. Stay productive.

Graphene Technologies – Managed IT Services, Cybersecurity, and Microsoft 365 Solutions for Houston Businesses

Download free HD stock image of Technology Light

Small Business Cybersecurity in 2026: 5 Security Layers Houston Companies Need


Many small businesses believe they have good cybersecurity because they already use antivirus software, firewalls, or multi-factor authentication. However, security problems usually happen when those tools do not work together as one complete system.

Over time, businesses often add security tools one by one. For example, they may add a new cybersecurity product after a client request or after hearing about a new threat. As a result, many companies end up with a patchwork of systems that leave important gaps behind.

Some security controls overlap. Others are missing completely.

Unfortunately, businesses usually do not notice those weaknesses until a cyberattack causes downtime, data loss, or expensive recovery costs.

That is why small businesses in Houston need a layered cybersecurity strategy that focuses on prevention, detection, response, and recovery.

At Graphene Technologies, we help Houston businesses strengthen cybersecurity with managed IT services, endpoint protection, cloud security, and proactive cybersecurity strategies built for modern threats.

Why Layered Cybersecurity Matters in 2026

Cyber threats are becoming more advanced every year. In addition, artificial intelligence is making phishing attacks, malware, and cyber scams faster and harder to detect.

Today, attackers do not rely on one method. Instead, they look for the easiest weakness in your environment.

For example, cybercriminals may target:

  • Weak passwords
  • Outdated devices
  • Unpatched software
  • Poor email security
  • Missing monitoring systems
  • Unsecured remote access

Because of this, businesses can no longer depend on one security tool to stop every threat.

Instead, companies need multiple security layers working together.

A layered cybersecurity strategy helps businesses:

  • Reduce ransomware risks
  • Improve data protection
  • Prevent unauthorized access
  • Detect suspicious activity faster
  • Improve business continuity
  • Strengthen compliance

Most importantly, layered security reduces the chance that one small mistake turns into a major cyber incident.

A Simple Way to Understand Cybersecurity Coverage

The easiest way to improve cybersecurity is to focus on outcomes instead of products.

The NIST Cybersecurity Framework helps businesses organize security into six main areas:

  • Govern
  • Identify
  • Protect
  • Detect
  • Respond
  • Recover

In simple terms, businesses should ask:

  • Who manages cybersecurity decisions?
  • What systems and data need protection?
  • What controls reduce cyber risks?
  • How quickly can threats be detected?
  • What happens during a cyberattack?
  • How fast can operations recover?

Many businesses focus heavily on protection tools. However, they often overlook detection, response, and recovery planning.

That creates major cybersecurity gaps.

5 Cybersecurity Layers Small Businesses Often Miss

Improving these five security layers can make your business more secure, more reliable, and easier to protect long term.

1. Phishing-Resistant Authentication

Multi-factor authentication (MFA) is important. However, basic MFA alone may not stop modern phishing attacks.

Cybercriminals now use fake login pages and social engineering to bypass weak authentication methods.

Because of this, businesses should:

  • Require MFA for all users
  • Protect administrator accounts first
  • Remove outdated login methods
  • Use risk-based login controls
  • Monitor suspicious sign-in activity

Strong identity protection helps stop attackers before they access company systems.

At Graphene Technologies, we help Houston businesses implement secure authentication systems that improve access security and reduce cyber risks.

2. Device Security and Usage Policies

Many businesses manage devices, but they do not clearly define what counts as a trusted device.

As a result, employees may connect personal devices that do not meet security standards.

Businesses should:

  • Create device security requirements
  • Set clear BYOD (Bring Your Own Device) policies
  • Require device compliance checks
  • Block risky or outdated devices
  • Monitor endpoint security continuously

This helps businesses reduce risks caused by unmanaged or vulnerable devices.

3. Email Security and User Protection

Email remains one of the biggest cybersecurity risks for small businesses.

Unfortunately, employee training alone is not enough to stop phishing attacks.

Businesses also need built-in email security protections such as:

  • Spam filtering
  • Link scanning
  • Attachment protection
  • Impersonation detection
  • External sender warnings

In addition, businesses should make it easy for employees to report suspicious emails without fear of blame.

Layered email protection helps reduce human error and prevent account compromise.

4. Continuous Patch Management

Many businesses assume patching is complete simply because updates are enabled. However, patch failures and missed updates are common.

Cybercriminals actively target:

  • Outdated operating systems
  • Unpatched applications
  • Old firmware
  • Vulnerable third-party software

Because of this, businesses should:

  • Set patching schedules
  • Prioritize critical vulnerabilities
  • Monitor patch failures
  • Update third-party applications
  • Review exceptions regularly

Consistent patch management helps eliminate known security gaps before attackers can exploit them.

5. Detection and Incident Response Readiness

Many businesses receive cybersecurity alerts. However, they often lack a clear plan for responding to those alerts quickly.

That creates delays during security incidents.

Businesses should:

  • Use endpoint detection and response (EDR)
  • Monitor networks continuously
  • Create incident response procedures
  • Define escalation rules
  • Test recovery plans regularly

As a result, businesses can contain threats faster and reduce operational downtime.

Why Houston Businesses Need Proactive Cybersecurity

Small businesses are frequent cyberattack targets because many lack dedicated cybersecurity teams.

At the same time, cyber threats continue to grow more advanced and automated.

For Houston businesses, proactive cybersecurity helps:

  • Reduce ransomware risks
  • Protect customer data
  • Improve compliance
  • Prevent downtime
  • Support business continuity
  • Reduce long-term IT costs

Businesses that strengthen cybersecurity early are often much better prepared when threats occur.

How Graphene Technologies Helps Businesses Improve Cybersecurity

At Graphene Technologies, we help Houston businesses build stronger cybersecurity foundations through:

  • Managed IT services
  • Endpoint protection
  • Cloud security
  • Cybersecurity monitoring
  • Backup and disaster recovery
  • Identity and access management
  • Network security solutions
  • Employee cybersecurity training

Our goal is to create practical cybersecurity strategies that improve protection without adding unnecessary complexity.

Strengthen Your Cybersecurity Strategy Today

Cybersecurity works best when businesses build consistent, layered protection across users, devices, networks, and data.

The good news is that businesses do not need to fix everything at once.

Instead, start with the weakest area, improve it, and then continue building stronger security layers over time.

At Graphene Technologies, we help Houston businesses identify cybersecurity gaps, improve protection, and build long-term security strategies that support business growth.

If your business needs help improving cybersecurity, reducing ransomware risks, or strengthening IT security controls, contact our team today to schedule a consultation.


A combination lock rests on a computer keyboard.

Ransomware Defense Plan: How Houston Businesses Can Prevent Cyber Attacks in 2026

Ransomware attacks are becoming more common, especially for small and mid-sized businesses. However, ransomware rarely starts with a major system failure. In most cases, it begins with something simple, like a stolen password or a phishing email.

Then, over time, attackers move deeper into the network. They steal data, gain access to more systems, and eventually lock files with ransomware encryption.

By the time businesses notice the attack, recovery can become expensive and stressful.

That is why every company needs a strong ransomware defense plan. The goal is not just to stop malware. Instead, the goal is to prevent attackers from gaining access in the first place.

At Graphene Technologies, we help Houston businesses improve cybersecurity, reduce ransomware risks, and strengthen business continuity with managed IT and cybersecurity services.

Why Ransomware Is So Dangerous for Businesses

Modern ransomware attacks are more advanced than ever before.

Today, cybercriminals often follow a step-by-step process:

  • Steal login credentials
  • Access company systems
  • Move across the network
  • Steal sensitive data
  • Encrypt files
  • Demand ransom payments

As a result, ransomware attacks can shut down operations for days or even weeks.

For Houston businesses, the impact can include:

  • Lost revenue
  • Downtime
  • Data breaches
  • Compliance violations
  • Damage to customer trust
  • Expensive recovery costs

Because of this, businesses need proactive cybersecurity protections instead of waiting until an attack happens.

5-Step Ransomware Defense Plan for Small Businesses

This ransomware defense plan helps businesses reduce cyber risks, improve security, and recover faster if an attack occurs.

Step 1: Use Strong Multi-Factor Authentication (MFA)

Most ransomware attacks begin with stolen passwords. Therefore, businesses should never rely on passwords alone.

Instead, companies should use:

  • Multi-factor authentication (MFA)
  • Strong password policies
  • Conditional access controls
  • Secure identity management

In addition, businesses should protect remote access systems and administrator accounts first.

MFA makes it much harder for attackers to access business systems, even if passwords are stolen.

At Graphene Technologies, we help Houston businesses deploy secure authentication systems that improve cybersecurity and reduce unauthorized access.

Step 2: Limit User Access Across the Network

Not every employee needs access to every system.

That is why businesses should follow the principle of least privilege. In simple terms, employees only get access to the data and systems they need for their jobs.

Businesses should also:

  • Separate admin accounts from daily user accounts
  • Remove shared logins
  • Limit administrator privileges
  • Restrict remote access permissions

As a result, businesses can reduce the damage caused by compromised accounts.

Step 3: Keep Systems and Software Updated

Outdated software is one of the biggest cybersecurity risks for businesses.

Cybercriminals often target:

  • Old operating systems
  • Unpatched software
  • Remote desktop systems
  • Unsupported applications

Because of this, businesses should create a patch management plan that includes:

  • Automatic updates
  • Fast security patching
  • Third-party software updates
  • Regular vulnerability reviews

Closing known security gaps helps stop ransomware attacks before they begin.

Step 4: Monitor for Suspicious Activity

The sooner businesses detect ransomware activity, the faster they can respond.

Therefore, businesses should use:

  • Endpoint detection and response (EDR)
  • Security monitoring tools
  • Threat alerts
  • Activity logging
  • Network monitoring

These tools help identify unusual behavior before ransomware spreads across the network.

In addition, managed cybersecurity services provide around-the-clock monitoring and faster incident response.

Step 5: Maintain Secure and Tested Backups

Backups are one of the most important parts of a ransomware defense plan.

However, backups only work if they are protected and tested regularly.

Businesses should:

  • Store backups offsite
  • Keep backup copies isolated
  • Test recovery processes often
  • Create disaster recovery plans
  • Define recovery priorities ahead of time

As a result, businesses can recover faster without paying ransom demands.

Common Cybersecurity Weak Points That Lead to Ransomware

Many ransomware attacks succeed because businesses overlook simple security issues.

Some of the most common problems include:

  • Weak passwords
  • Missing MFA
  • Outdated systems
  • Poor employee cybersecurity training
  • Unsecured remote access
  • Inadequate backups
  • Lack of endpoint protection

Fortunately, fixing these issues can significantly reduce ransomware risks.

Why Houston Businesses Need Managed Cybersecurity Services

Many small businesses do not have the internal resources needed to manage cybersecurity threats full-time.

As cyber threats continue to grow, businesses need proactive IT support and security monitoring.

At Graphene Technologies, we help Houston businesses improve ransomware protection with:

  • Managed IT services
  • Endpoint security
  • Backup and disaster recovery
  • Cloud security solutions
  • 24/7 cybersecurity monitoring
  • Employee cybersecurity training
  • Network security management

Our goal is to help businesses reduce downtime, improve security, and protect critical data.

Build a Stronger Ransomware Defense Plan Today

Ransomware attacks can happen to businesses of any size. However, the companies that prepare early are much more likely to recover quickly.

A proactive ransomware defense plan helps businesses:

  • Reduce cybersecurity risks
  • Improve business continuity
  • Protect customer data
  • Prevent downtime
  • Strengthen compliance

At Graphene Technologies, we help Houston businesses build practical cybersecurity strategies that improve protection without slowing operations.

If your business needs help improving ransomware protection, securing backups, or strengthening cybersecurity defenses, contact our team today to schedule a consultation.

Free castle security locked vector

Zero Trust Security in Houston

Why Houston Businesses Are Moving to Zero Trust Security

Think about your office building. You have locks, maybe cameras, maybe security staff.

But once someone gets inside, can they access everything?

That’s how traditional networks work. One login often opens the door to multiple systems. And that’s exactly what cybercriminals rely on.

At Graphene Technologies in Houston, we help businesses move beyond this outdated model with Zero Trust security.

What Is Zero Trust Security?

Zero Trust is simple in concept:

Never trust. Always verify.

Every user, device, and access request is treated as untrusted until proven otherwise. It doesn’t matter if the request comes from inside or outside your network.

For Houston businesses using cloud platforms and remote work, this approach is no longer optional. It’s essential.

Why Traditional Network Security No Longer Works

The old model assumed that once someone was inside your network, they were safe.

That’s no longer true.

Today’s threats include:

  • Stolen credentials from phishing attacks
  • Malware already inside your system
  • Insider threats (intentional or accidental)

Once attackers get in, they can move freely across systems.

Zero Trust stops that movement by verifying every step.

The Core Principles of Zero Trust Security

At Graphene Technologies Houston, we implement Zero Trust using two key strategies:

Least Privilege Access

Users only get access to what they need, nothing more.

For example:

  • A marketing employee shouldn’t access financial systems
  • Applications shouldn’t communicate unless necessary

This reduces risk dramatically.

Micro-Segmentation

Your network is divided into secure sections.

If one area is compromised, the threat is contained.

For example:

  • Guest Wi-Fi is separated from internal systems
  • Critical data is isolated from general access

This prevents attackers from spreading across your network.

How Houston Businesses Can Start with Zero Trust

You don’t need to rebuild your entire IT environment overnight.

Start with these practical steps:

1. Protect Critical Data First

Identify where your most sensitive data lives and secure it first.

2. Enable Multi-Factor Authentication (MFA)

MFA is one of the most effective cybersecurity tools available.

Even if a password is stolen, access is blocked without verification.

3. Segment Your Network

Separate critical systems from general access networks.

This limits the impact of any breach.

Tools That Make Zero Trust Easier

Modern platforms already support Zero Trust principles.

We help Houston businesses configure:

  • Microsoft 365 and Google Workspace security settings
  • Conditional access policies
  • Device and identity verification controls

We also implement advanced solutions like:

  • Secure Access Service Edge (SASE) for cloud-based protection
  • Centralized identity and access management

Build a Stronger Cybersecurity Culture

Zero Trust isn’t just technology. It’s a mindset shift.

It requires:

  • Ongoing monitoring
  • Regular access reviews
  • Clear policies for who can access what

Your team may need time to adjust, but the result is a much stronger security posture.

Your Path to Zero Trust Security in Houston

Start with:

  • A full access and data audit
  • Enforcing MFA across all systems
  • Segmenting high-value assets
  • Leveraging built-in cloud security tools

Zero Trust is not a one-time project. It’s an ongoing strategy that grows with your business.

Secure Your Houston Business with Graphene Technologies

If your current network still relies on “trusted access,” you’re at risk.

Graphene Technologies helps Houston businesses:

  • Implement Zero Trust security frameworks
  • Secure cloud and on-premise systems
  • Reduce breach risk and lateral movement
  • Strengthen overall cybersecurity posture


Contact Graphene Technologies today to schedule your Zero Trust readiness assessment and protect your business from modern cyber threats.


Free sign security coat of arms vector

Houston Vendor Risk Management & Cybersecurity Services

The Hidden Cybersecurity Risk for Houston Businesses: Your Vendors

You’ve invested in cybersecurity. Firewalls are in place. Your team is trained. Everything seems secure.

But what about your vendors?

Your accounting firm, cloud provider, or marketing platforms all have access to your business in some way. And if their security is weak, your business is exposed.

At Graphene Technologies in Houston, we help businesses uncover and manage these hidden risks before they turn into serious breaches.

What Is Supply Chain Cybersecurity and Why It Matters

Every vendor you work with is a potential entry point into your systems.

Cybercriminals often target smaller, less secure vendors because they’re easier to breach. Once inside, they use that trusted connection to access larger, more secure organizations.

This is known as third-party cyber risk, and it’s one of the fastest-growing threats for Houston businesses.

The Real Impact of a Vendor Security Breach

When a vendor is compromised, the damage doesn’t stop with them. It spreads to you.

Here’s what Houston businesses risk:

  • Exposure of customer and financial data
  • Loss of intellectual property
  • Regulatory fines and compliance violations
  • Damage to your reputation
  • Costly incident response and recovery

Operationally, it gets worse. Your internal IT team may spend days or weeks responding to a breach that didn’t even start in your environment.

How Graphene Technologies Helps Houston Businesses Reduce Vendor Risk

At Graphene Technologies Houston, we take a proactive approach to vendor risk management.

We don’t rely on assumptions. We verify security.

Our process includes:

Vendor Security Assessments

We evaluate your vendors’ cybersecurity posture by reviewing:

  • Security certifications (SOC 2, ISO 27001)
  • Data handling and encryption practices
  • Breach notification policies
  • Employee access controls
  • Penetration testing and monitoring

Continuous Vendor Monitoring

Cyber risk isn’t static. We continuously monitor your vendors for:

  • Data breaches
  • Security rating changes
  • Emerging vulnerabilities

This ensures you’re never caught off guard.

Contract & Compliance Protection

We help you strengthen vendor agreements with:

  • Defined cybersecurity requirements
  • Right-to-audit clauses
  • Clear breach notification timelines (24–72 hours)

This turns expectations into enforceable protection.

Practical Steps to Strengthen Your Vendor Ecosystem

If you’re not sure where to start, here are key steps we recommend for Houston businesses:

1. Inventory All Vendors

Identify every vendor with access to your systems or data.

2. Assign Risk Levels

Classify vendors based on access:

  • High risk: Direct system or admin access
  • Medium risk: Limited system interaction
  • Low risk: Minimal or no access

3. Evaluate Security Practices

Send security questionnaires and review policies carefully.

4. Reduce Single Points of Failure

Avoid relying on one vendor for critical services whenever possible.

Turn Your Vendor Network into a Security Advantage

Vendor risk management isn’t about distrust. It’s about accountability.

When you raise your cybersecurity standards, your vendors follow. That creates a stronger, more secure business ecosystem.

For Houston companies, this is no longer optional. It’s a critical part of doing business safely.

Protect Your Houston Business with Graphene Technologies

Don’t let a vendor become your weakest link.

Graphene Technologies provides Houston businesses with:

  • Vendor risk assessments
  • Ongoing cybersecurity monitoring
  • Compliance support
  • End-to-end IT security solutions

Contact Graphene Technologies today to assess your vendors and build a stronger, more secure supply chain.


Free read only readonly locked vector

Secure Remote Work with Graphene Technologies Houston IT Security

Graphene Technologies Houston IT security helps businesses protect sensitive data while employees work from anywhere. Today, remote work extends beyond the office into homes, coffee shops, and shared spaces. However, these environments introduce serious risks. Therefore, companies must act quickly to strengthen their cybersecurity strategies.

As remote work continues to grow, businesses need clear policies and strong tools. Otherwise, employees may unknowingly expose company data. Fortunately, Graphene Technologies delivers reliable solutions that keep your workforce secure in every location.

The Risks of Public Wi-Fi Networks

Public Wi-Fi attracts remote workers because it is convenient and free. However, it also creates major security vulnerabilities. In many cases, these networks lack encryption. As a result, attackers can intercept data within seconds.

Moreover, cybercriminals often create fake networks that appear legitimate. For example, a network labeled “Free Coffee Shop Wi-Fi” may actually belong to a hacker. Once an employee connects, the attacker can monitor activity and steal credentials.

Therefore, businesses must train employees to avoid unsecured networks. Even password-protected Wi-Fi can pose risks if widely shared. Instead, companies should enforce strict usage policies to reduce exposure.

Why VPNs Are Essential for Remote Security

A Virtual Private Network (VPN) protects data by encrypting internet traffic. Because of this, hackers cannot read sensitive information. For this reason, VPN usage should be mandatory for all remote employees.

In addition, companies should configure VPNs to connect automatically. This step removes user error and ensures consistent protection. At Graphene Technologies, we help Houston businesses deploy secure, easy-to-use VPN solutions.

Furthermore, technical controls can block access to company systems without a VPN. This approach guarantees compliance and strengthens your overall security posture.

Prevent Visual Hacking in Public Spaces

While digital threats increase, physical risks also remain. For instance, someone nearby can easily view a laptop screen. This tactic, known as visual hacking, requires no technical skill.

Therefore, employees must stay aware of their surroundings. Sensitive data, such as financial reports or client records, should never be visible in public. To reduce this risk, businesses should provide privacy screen filters.

Additionally, employees should position screens away from others whenever possible. These simple steps significantly improve data protection.

Strengthen Physical Device Security

Employees often underestimate the risk of device theft. However, leaving a laptop unattended in a public place invites trouble. Thieves act quickly, especially in busy environments.

To prevent this, employees must keep devices within reach at all times. Moreover, using cable locks adds an extra layer of protection. Although not foolproof, these tools discourage opportunistic theft.

At the same time, awareness plays a key role. When employees stay alert, they can identify and avoid risky situations.

Protect Conversations and Sensitive Information

Even in noisy environments, conversations can be overheard. Therefore, discussing confidential information in public creates unnecessary risk.

Instead, employees should move to private areas when handling sensitive calls. For example, stepping outside or sitting in a car offers more privacy. While headphones help, they do not prevent others from hearing one side of the conversation.

Consequently, clear communication guidelines must be part of your remote work policy.

Build a Clear Remote Work Security Policy

A strong policy removes confusion and sets expectations. Employees need clear instructions on how to handle public Wi-Fi, devices, and conversations.

In addition, businesses should explain why each rule matters. When employees understand the risks, they are more likely to comply. Graphene Technologies helps Houston companies create effective, easy-to-follow security policies.

Moreover, companies should review policies regularly. As threats evolve, your strategy must adapt. Updating guidelines ensures long-term protection.

Empower Your Workforce with Graphene Technologies Houston IT Security

Remote work offers flexibility, but it also demands responsibility. Therefore, businesses must invest in the right tools and training.

Graphene Technologies Houston IT security provides comprehensive solutions that protect your business from modern threats. From secure remote access to employee training, we help you stay ahead of cyber risks.

If your team works remotely, now is the time to act. Strengthen your defenses and protect your data—no matter where your employees log in.